

Euronews reports that Sweden has restricted browser-based access to ChatGPT and Claude on government work computers. The stated concerns are sensitive data, information security and the use of AI tools without appropriate agreements.
Microsoft Copilot remains an approved alternative under government security arrangements. Read the report.
Whatever you think of the decision, the underlying question applies to every CIO, CISO and digital transformation leader.
Should an organisation block AI, or build a secure framework for adopting it responsibly?
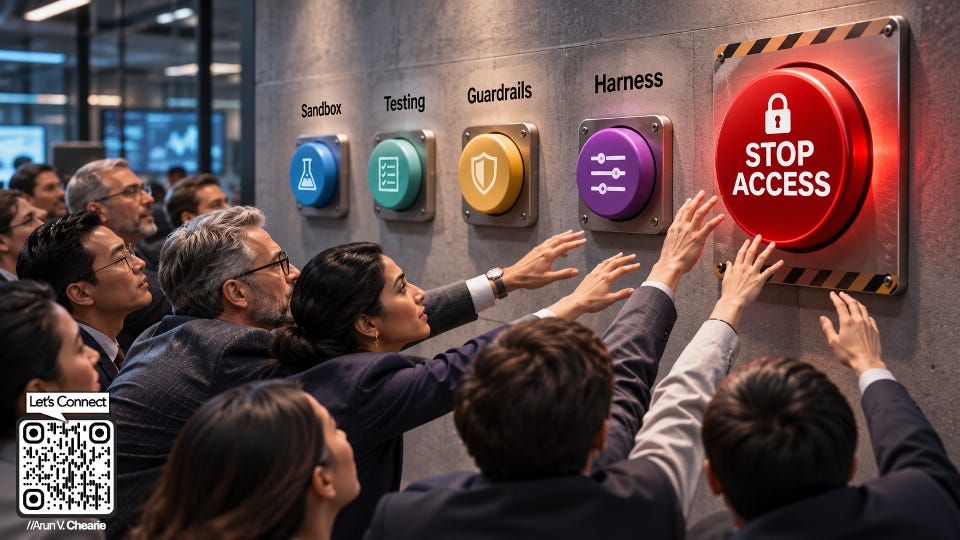
A ban is a defensible answer when you don’t yet understand the risk. It is a poor long-term strategy if the risk could be managed through procurement, technical controls, training and clear policy.
The more I think about this, the more alternatives emerge. Slamming the stop button should be the last resort.
Here are five routes worth evaluating first.
1. Enterprise AI Subscriptions
Compare business-grade offerings such as ChatGPT Business or Enterprise, Claude for Work and Microsoft 365 Copilot. They differ in administrative controls, contractual data protections and security features. The right choice depends on your compliance obligations, how you configure the product and how much risk you are prepared to carry.
2. An Organisation-controlled AI gateway
Rather than letting staff visit multiple AI websites directly, route requests through an approved platform that handles authentication, access control, logging and policy enforcement. You gain visibility without giving up the ability to use different models for different tasks.
3. Risk-based access policies
Not all data carries the same risk, so not all data needs the same rule.
🟢 Public information: approved AI tools permitted.
🟡 Internal business information: approved enterprise environments only.
🔴 Confidential, personal or classified information: restricted workflows, with explicit authorisation and safeguards.
Tiers also make training easier. Staff can remember three categories far more readily than a forty-page policy.
4. Private-cloud or Self-hosted AI
For the most sensitive workloads, consider models deployed in a controlled cloud environment or on infrastructure you manage. This gives you more control over deployment and data flows. It also requires security expertise, ongoing maintenance, model governance and a budget that continues after launch.
5. A controlled pilot before full rollout
Run a time-bound pilot with selected teams. Test data handling, access controls, auditability, output quality, adoption and total cost of ownership before deciding what to approve.
Your assessment should cover contractual terms, retention and deletion policies, data residency, third-party integrations, incident response and regulatory obligations. A vendor stating that it does not train on customer data answers only one of those questions.
So… In essence.
A ban can work as an immediate safeguard. The trouble is that it settles the access question without settling the risk question. Staff who see value in these tools may look for ways around the restriction, and an approved route with logging is easier to govern than an unapproved one you cannot see.
The aim is not unrestricted access to every model. It is giving employees the right AI tools for the right tasks, under controls matched to the sensitivity of the data.
Over to you now.
If you had to decide for your organisation today, would you choose a single approved AI platform, a multi-model enterprise gateway, or a private deployment? I’d like to hear what is driving your answer, especially if you work in a regulated sector.